
Docker and Google Release Agent Orchestration and Sandboxing Tools
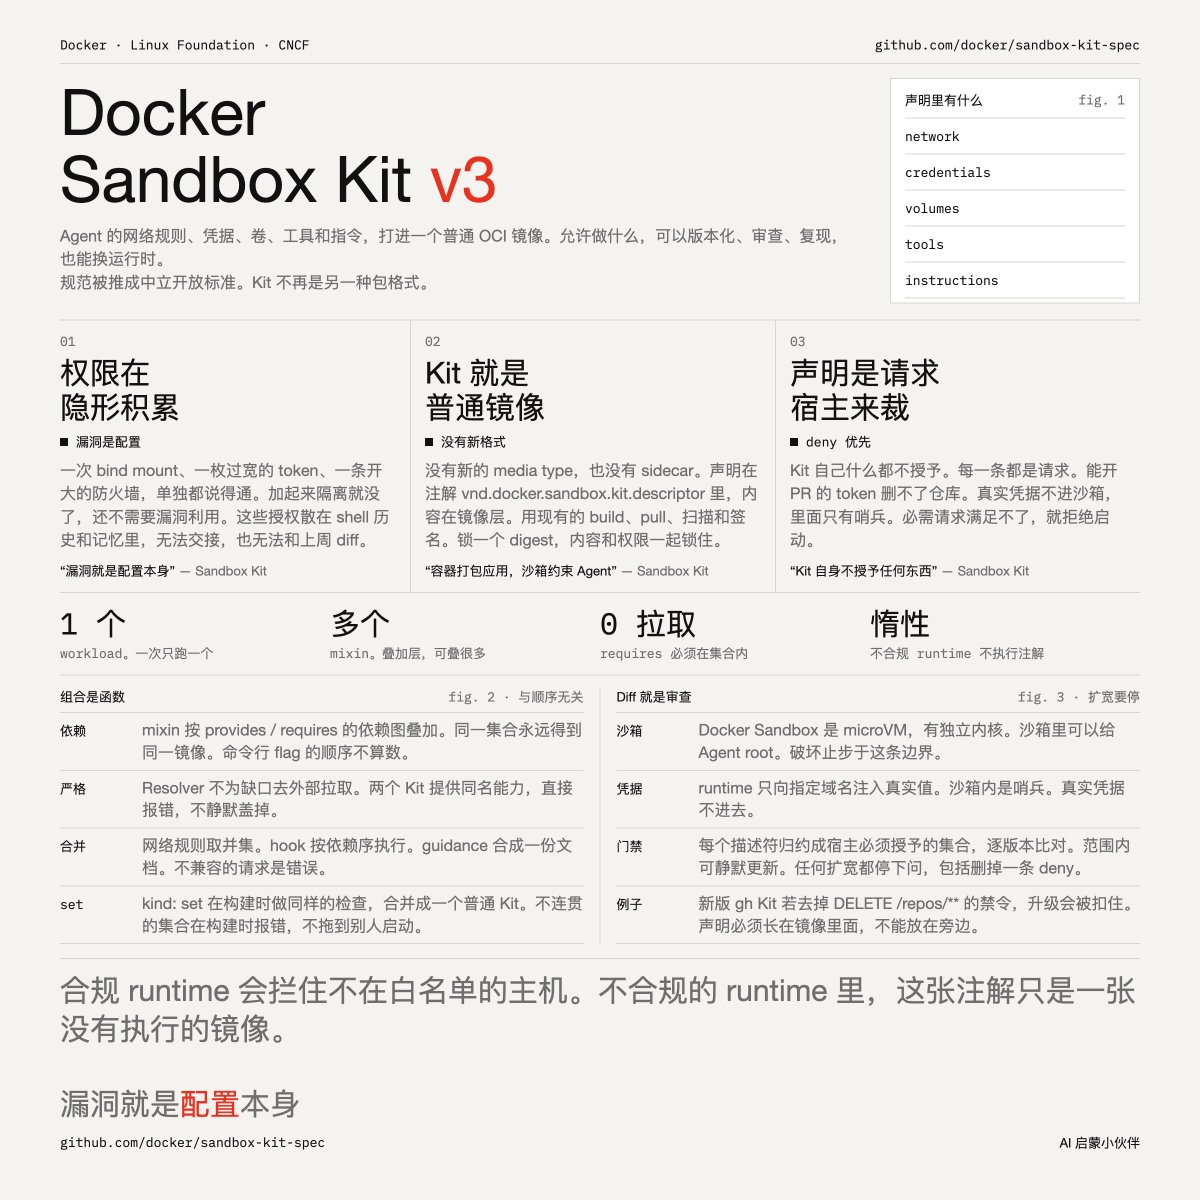
Docker released Sandbox Kit v3, a standard OCI image format for declaring agent permissions, making them versionable and auditable. Google open-sourced AX, a declarative orchestration runtime for agent workloads, using YAML to define tasks, workspaces, and models. Both tools address the challenge of running AI agents securely and at scale.
Key insights
Docker Sandbox Kit v3: Agent Permissions as OCI Images
Docker's Sandbox Kit v3 packages agent permissions (network rules, credentials, volumes, tools) into a standard OCI image. Kits are built with docker buildx, pulled with docker pull, and can be signed and scanned. They use microVM isolation with independent kernels. Permissions are declared as 'asks' that the host runtime must satisfy; deny rules take precedence. Mixins allow composable permission layers with dependency resolution.
Google AX: Declarative Orchestration for Agent Workloads
Google's AX is a Kubernetes-like runtime for agents, using YAML to define Tasks (isolated sandboxes), Workspaces (declarative environment setup including generative workspaces), and Models (named resources with API keys). It uses four binaries: ax CLI, ax-server, ax-controller, and ax-task-runner. Security features include guest service disabled by default, explicit allowlist for outbound traffic, and credential injection via Gateway.
Zuse: Open-Source Devin with Unified Agent Interface
Zuse is an open-source project that wraps multiple coding agents (Claude Code, Codex, Grok, etc.) into a unified, persistent, project-aware GUI. It addresses tool fragmentation, context loss, and human bottleneck by providing a streaming timeline, SQLite persistence, and cloud workspaces with mobile notifications. It uses a provider process lifecycle with separate management and session planes, and a strict single data flow architecture.